
Core Lightning crash can persist after an upgrade
A disclosed flaw in Core Lightning, software for Bitcoin’s Lightning payment network, can leave a node crashing on restart even after an upgrade because the malicious announcement that triggered it remains on disk.
Researcher Nishant Bansal’s October 24 disclosure identifies versions v25.02 through v26.04 as affected. Once the announcement is saved, restarting reloads the same trigger. Bansal says the operator must manually remove the offending record to restore the node.
Bitcoin Optech highlighted the issue on October 30, but the preventive patch is months old. Core Lightning merged PR #9082 on April 24 and shipped the fix in v26.04.1 on April 25. The October disclosure explains a flaw whose preventive fix had been available since April.
Why the patch does not clear a stored trigger
Channel announcements tell nodes about connections in the Lightning routing graph. In this case, an announcement named the same previously unknown node as both endpoints. Vulnerable software accepted it and wrote it to its on-disk gossip_store before loading it into the routing graph.

The graph then tried to insert that node twice. A safeguard against duplicates aborted gossipd, the component handling these announcements, and Core Lightning treated that failure as fatal to the whole node.
The patch checks the endpoint ordering before accepting an announcement. Requiring the first node ID to be strictly less than the second also rejects equal IDs. This stops the malformed input from being accepted and stored.
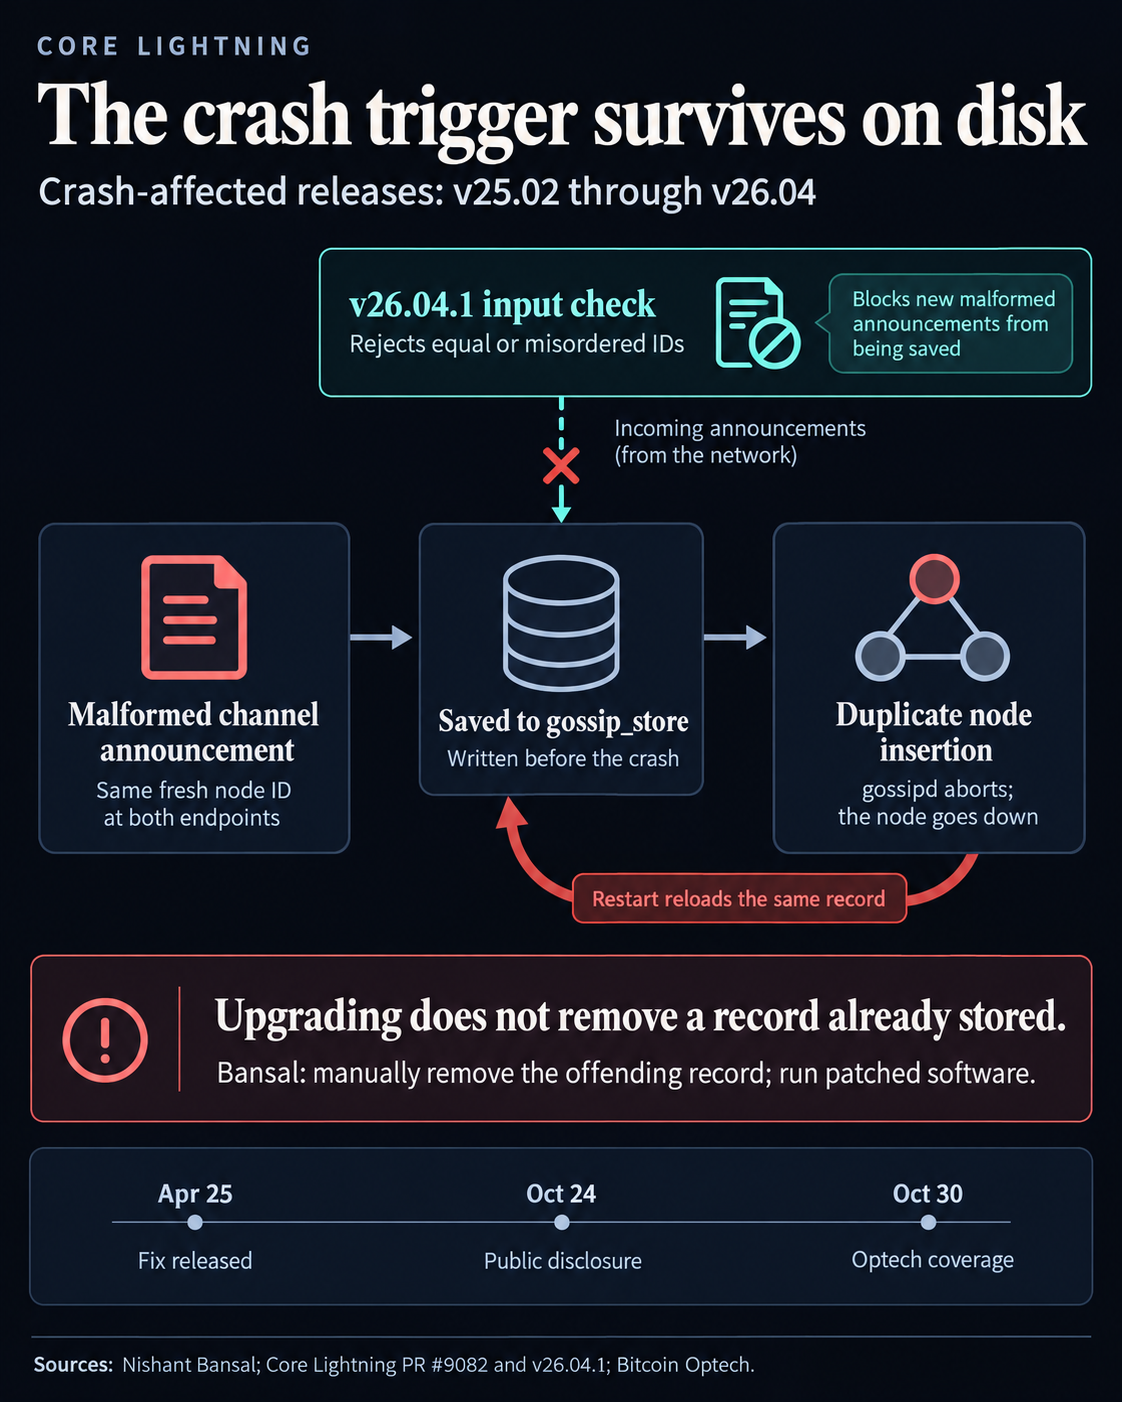
The new validation check applies to incoming announcements. Startup still reads records already in gossip_store, and upgrading does not remove the malicious record saved before the crash.
Bansal’s recovery requirement is manual removal of the malicious record from gossip_store. Cleanup alone also leaves a vulnerable installation open to another crash: the disclosure says an attacker can resend the same announcement while the attacker-controlled funding output remains unspent.
Bitcoin Optech notes that Core Lightning releases before v25.02 could accept and relay such announcements without crashing themselves. An attacker therefore did not need a direct connection to every vulnerable node.
For operators choosing an upgrade now, v26.04.1 marks the first fix for this defect. As of November 2, the project’s latest release is v26.06.9, issued October 7, which maintainers strongly recommend installing.
Downtime carries a payment-monitoring risk beyond unavailable service. Bansal warns that an offline node cannot watch the chain for a revoked channel state or a time-limited payment claim that must be made before expiry. Missing those events can put funds at risk.